
Background
We treat a System of Systems (SoS) as a social system in which autonomous actors make decisions and interact. The behavior of such large socio-technical systems cannot be explained by checking each component in isolation.
Our goal is to establish engineering methods for designing the behavior of the whole system. These methods cover structure and connectivity as well as the interactions, incentives, and decisions of the participating actors, and they are used to explain, design, and validate the intended system-wide behavior.
The challenge
Modern systems such as automated road traffic, smart grids, smart cities, and data-sharing infrastructures are increasingly distributed systems in which multiple actors make decisions independently. Even when each actor behaves rationally, their interaction can still produce outcomes at the level of the whole system that no one intended.
- Self-interested behavior can reduce overall efficiency, as seen in traffic congestion or peak electricity demand.
- Unexpected interactions can destabilize the system as a whole.
- Even when each individual subsystem is locally optimal, the overall system may still fail to function well.
Limits of previous research
Conventional systems engineering and System of Systems Engineering (SoSE) have addressed areas such as architecture design, communication and control, and software design. However, they have not fully addressed one of the most important questions in real-world SoS: how the participating actors actually behave.
As a result, a system may be architecturally correct and implemented according to specification, yet still fail to work as intended in practice. To make SoS function in real society, the decision-making and interaction among its actors must be designed in addition to the structure of the system.
What we do
Rather than controlling the system from the outside, we design it so that desirable behavior is naturally selected. Concretely, we design rules, contracts, and incentives so that even when each actor acts autonomously, the system as a whole converges to a desirable state.
In other words, we design the conditions under which the interaction of independent actors yields a desirable equilibrium. Treating SoS as socio-technical systems extends engineering from structural design to behavioral and institutional design.
Achievements so far
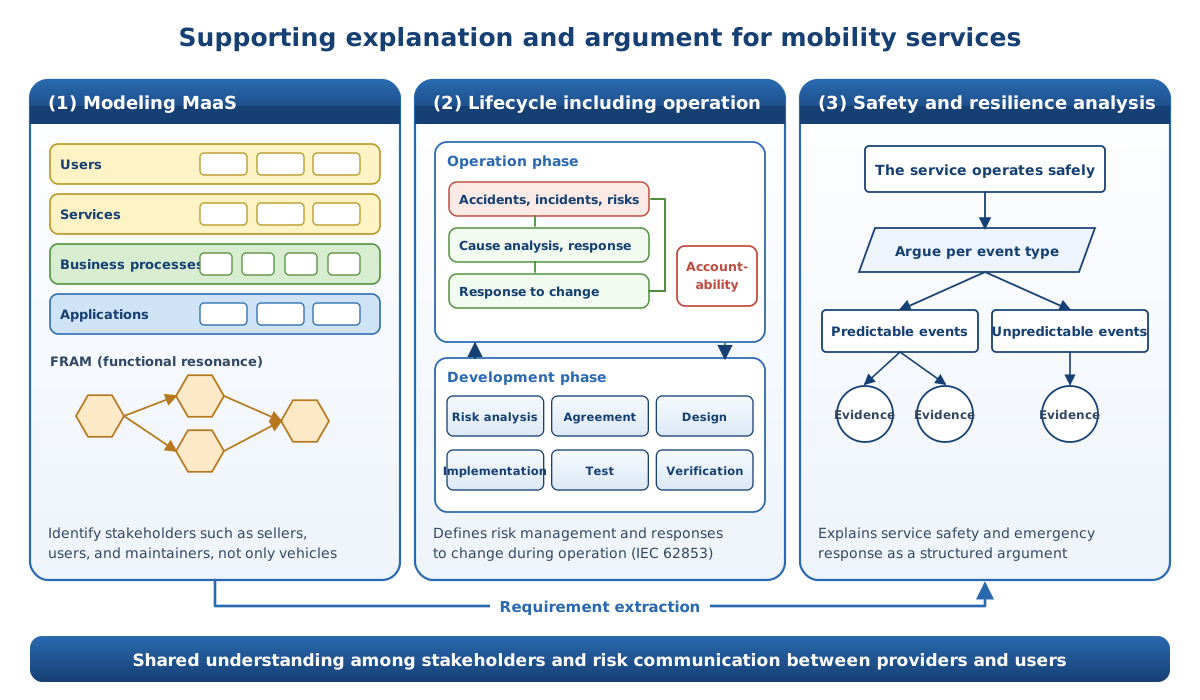
This theme grew out of resilience research on Mobility-as-a-Service: resilience analysis and design for MaaS based on enterprise architecture modeling (Reliability Engineering & System Safety, 2023), reliability analysis of digital healthcare services using semi-quantitative functional resonance analysis (Computer Systems Science and Engineering, 2023), and, more recently, a multi-agent reinforcement learning based resilience engineering method for MaaS (IEEE Transactions on Network and Service Management, 2026).
For assuring SoS as a whole, the methods have expanded from modeling to game theory: consensus-based resilience assurance (IEEE Access, 2025), an ArchiMate-based evaluation approach (Systems, 2025), and dynamic resilience analysis based on Stackelberg evolutionary games (ICSRS 2025; SoSE 2026). An empirical study treating governance as a structural design variable (SoSE 2026) shows how this theme extends to institutional design.
The research is also connected to public activities, including the SEAMS and TIGARS projects on assurance for automated driving and standardization work around IEC 62853, with review articles such as one on comprehensive dependability for automated driving (Journal of Society of Automotive Engineers of Japan, 2024).
Why this matters
Services that involve many organizations, such as transport, energy, and logistics, cannot be improved by any single actor alone. As this research matures, rules and incentives can be designed so that participants cooperate naturally, and the service as a whole keeps running through disasters and failures.
We believe that designing the conditions under which the whole system moves in a desirable direction is effective for social systems that no single actor can control.
Where we are heading
We aim to make this equilibrium-based view of SoS design concrete and to establish practical foundations for design and validation in real-world settings. Through formalization of rules and contracts in Contract Architecture Description Language (CADL), design of dynamic adaptation under autonomous actors, evaluation of system-wide dependability, and empirical studies using digital twins, we aim to develop a methodology for SoS as socio-technical system design.
- Formalization and verification of rules and contracts: describe rules and contracts as well as system structure, and detect contradictions or inconsistencies at design time.
- Design of dynamic adaptation under autonomous actors: clarify mechanisms by which independently acting and learning actors can still lead the whole system toward desirable states.
- Evaluation of system-wide dependability: assess and mitigate problems caused by interaction across the whole system, in addition to component-level correctness.
Example thesis topics
Alongside the foundations described above, we work on the following kinds of topics. Students' thesis topics are usually chosen from within these directions, through discussion.
- Describing rules and contracts in the Contract Architecture Description Language (CADL) and verifying them at design time
- Dynamic resilience analysis of SoS based on Stackelberg and evolutionary games
- Empirical studies of governance as a design variable: trade-offs between performance and autonomy
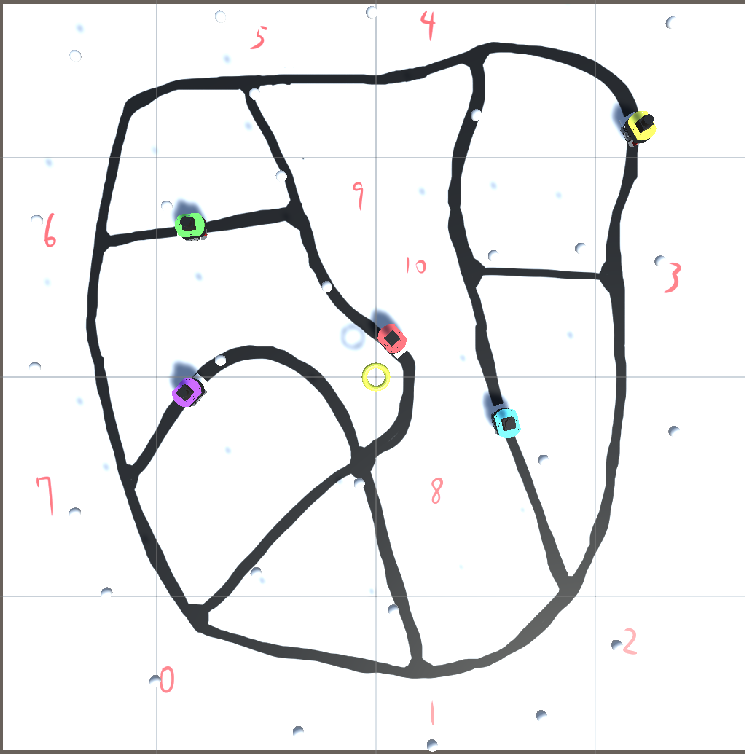
- Building SoS experiment environments with digital twins, such as robot simulators
- Case studies of real services: MaaS, airports, disaster response, and hazardous-material transport


